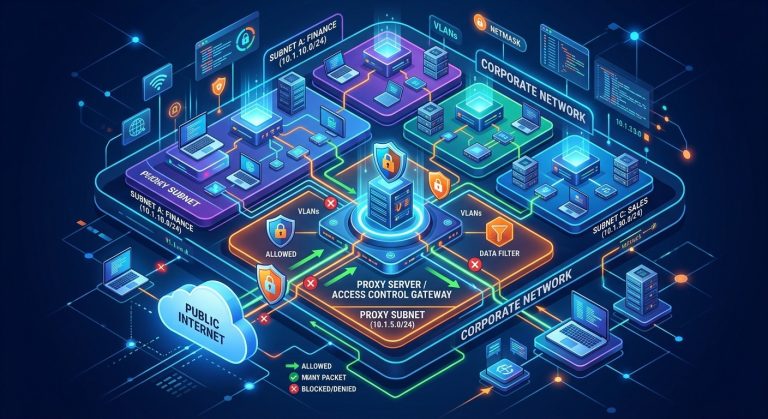
Managing proxy access for a corporate network of any real size is not something you can handle cleanly with individual IP addresses. When you have 300 workstations, a development cluster, a guest Wi-Fi segment, and a handful of executive devices, each with different internet access requirements, per-IP rules become a maintenance nightmare fast. Subnets fix this. They let you group machines logically, assign each group a CIDR block, and then target that entire block with a single ACL entry in your proxy. The result is a policy structure that stays manageable as your network grows and as staff move between teams or roles.
Subnet-based proxy ACLs replace fragile per-IP entries with scalable network blocks aligned to departments or security tiers. Before entering any range into a proxy config, confirm the subnet mask, broadcast address, and usable host count first. Getting the ranges right prevents overlap, accidental policy bypass, and rule conflicts that are hard to trace. This article covers how to structure your segments, calculate accurate ranges, and apply validated CIDR blocks in Squid and Microsoft Forefront TMG.
Why Per-IP Proxy Rules Become Unworkable Over Time
In a 20-person office, maintaining individual IP-based ACL entries is manageable. The real trouble starts as the network grows. New machines join, IP assignments shift (especially where DHCP is in play), and someone in finance ends up with a rule intended for engineering. You spend more time auditing the access list than enforcing actual internet policy.
Per-IP rules also create a false sense of precision. An IP address tells you where a packet originated, not what it represents organizationally. An address in the 10.0.1.0 range could belong to a developer, a contractor, or a building management sensor. Without a subnet structure that maps to real organizational segments, your proxy ACL has no reliable anchor. Policy enforcement becomes inconsistent, and demonstrating compliance during a security audit gets complicated fast. The fix is not better IP bookkeeping. The fix is subnets.
Designing Your Network Segments Around Access Control Needs
Before opening the proxy admin console, get the network map right. Segmenting by function or security tier is more durable than segmenting by physical location or switch port. A clean starting model typically includes a general staff segment, a finance segment, a server and infrastructure segment, a guest and BYOD segment, and a dedicated IT admin range. Each segment gets its own CIDR block and, in the proxy configuration, its own filter or bypass profile.
A security-tier model is worth considering in most corporate environments. Tiers can be based on data sensitivity, user privilege level, or risk profile. A finance subnet might get filtered browsing with strict content categories blocked. An IT admin subnet might get a bypass or reduced filtering profile for security tooling and research access. A guest subnet routes through a separate proxy path with heavy filtering, no access to internal resources, and bandwidth limits applied. The proxy enforces all of this through ACL rules targeting each CIDR block.
The key constraint is that segments must map to non-overlapping CIDR blocks. Overlapping ranges create rule ambiguity, and different proxy platforms resolve that ambiguity in different ways, sometimes silently applying the wrong policy to an entire host group with no error to alert you.
Calculating Host Ranges Before Entering Subnets Into Your Proxy
Once the segment design is on paper, the next job is translating it into CIDR notation that the proxy can use. This is where many admins run into problems. The formula for usable host addresses in a subnet is 2^(32 minus prefix length) minus 2, subtracting the network address and broadcast address. A /24 gives you 254 usable hosts. A /25 gives 126. A /26 gives 62. A /27 gives 30. Choosing the right prefix for each segment requires knowing your current host count and leaving reasonable headroom for growth.
If you are not comfortable doing this mentally, running your proposed ranges through a subnet calculator gives you the network address, broadcast address, full host range, and subnet mask in one pass. This is the right step to take before touching the proxy config, not after. Entering a /26 block into Squid when the department actually spans a /25 means roughly half your users fall outside the ACL match and receive default policy by accident, with no error message to explain why.
Document every block you plan to use in a simple reference sheet: segment name, CIDR block, intended proxy profile, responsible team, and last review date. This becomes both your configuration reference and your audit trail when questions arise later.
Building Subnet-Based ACL Rules in Squid
Squid handles subnet-based access control cleanly through the src ACL type, which accepts CIDR notation directly. The general approach is to define each subnet as a named ACL and then reference those names in your http_access directives. Rule order matters in Squid: the first matching rule wins, so structure your ACLs from most specific to most general.
For a typical layered setup, define your most trusted segments first (IT admin, security operations), then department-level segments with their respective profiles, then the general staff block, and finally a deny-all for anything that does not match. Named ACLs make the configuration readable and auditable. A rule named acl finance_subnet src 10.0.20.0/24 is immediately understandable in a configuration review. A rule targeting a raw IP range is not.
Squid also supports ACL files, where you list CIDR blocks line by line in an external text file and reference that file in the ACL definition. This is the right approach for large networks where the main config file would otherwise become unwieldy. Squid reloads the external file on a reconfigure command without a full service restart, which means you can update subnet lists during business hours with minimal disruption.
Subnet-Based Policy in Microsoft Forefront TMG
Microsoft Forefront TMG handles subnet-based access control through its network objects and access rule engine. Rather than raw CIDR entries in a config file, TMG uses a GUI-driven network object model where you define computer sets or IP address ranges and then reference those objects in access rules.
The relevant object type for subnet-based control is the Network object or IP Address Range, which you define in the Toolbox pane of the Firewall Policy section. For clean departmental segmentation, creating one network object per subnet with a descriptive name maps directly to your segment plan. Access rules can then target specific source network objects, apply proxy filter profiles, and chain to user authentication or time-of-day conditions for more granular control.
TMG policy order works the same way as Squid in one important respect: rules are evaluated top-to-bottom, first match wins. Place more specific subnet rules above broader catch-all rules to avoid unintended policy inheritance across segments.
Squid vs. Forefront TMG: Subnet ACL Feature Comparison
| Feature | Squid | Forefront TMG |
|---|---|---|
| CIDR entry method | Direct CIDR notation in config file or external ACL file | GUI-based network objects referencing IP address ranges |
| Rule order enforcement | First matching http_access directive wins |
Top-to-bottom rule evaluation, first match wins |
| Large subnet list handling | External ACL files, reload without service restart | Network object groups, exported and imported via XML |
| Audit trail | Config file version control (Git or equivalent) | Built-in audit log in TMG management console |
| Active Directory integration | Via Kerberos helper or external auth; not native | Native AD integration, user and group conditions in rules |
CIDR Notation Checklist and Validation Steps
Before committing subnet ranges to any proxy configuration, run through a structured validation process. Skipping this step is where most subnet-related proxy misconfigurations originate. Any entry that violates CIDR addressing rules will either fail silently or throw an error depending on the proxy platform, and neither outcome is easy to diagnose after the fact. The following steps should be completed for every subnet you plan to add to a proxy ACL:
- Confirm the network address is correctly written. The host bits of a valid network address must all be zero. 10.0.20.5/24 is malformed; 10.0.20.0/24 is correct. Most proxy platforms will reject the malformed entry, but some will silently truncate and apply an unexpected rule.
- Verify the host range against your actual device count. Use a subnet calculator to confirm the usable range covers all hosts in the segment and includes room for future growth. A /27 that fits today’s 28 devices leaves no room for two more hires next quarter.
- Check for overlap with existing ACL entries. Overlapping blocks cause one segment to inherit another segment’s policy. Export your full ACL list and compare ranges systematically before adding new entries.
- Confirm the prefix length is typed exactly. A /25 and a /26 differ by 64 addresses. One transposed digit places a significant number of hosts in the wrong policy tier with no warning from the proxy.
- Test the rule against a known host in the subnet. After applying the configuration, make a test request from a device within the target CIDR range and confirm the correct filter profile appears in the proxy access log.
- Document the change in your network segment registry. Record a date stamp, the CIDR block added, the profile applied, and the name of the person who made the change. This keeps your access control policy auditable over time.
From Network Design to Enforceable Policy
A proxy configuration built around subnet ACLs is significantly easier to audit than one built on individual IP entries. Each rule maps directly to an organizational segment, and the intent behind the rule is readable from the ACL name alone. When a security review comes around, you can produce a clear map from department to subnet to proxy profile, backed by documented validation steps and a change history.
The segment design itself should be reviewed at least annually, or any time the organizational structure changes meaningfully. Subnets assigned to departments that no longer exist, or that no longer reflect the correct host range, become silent policy gaps over time. A finance team that has grown from 28 people to 65 but still sits on a /27 is running outside its ACL boundary without anyone noticing.
Getting the groundwork right, mapping segments thoughtfully, validating every CIDR block before entry, and understanding how rule order affects enforcement in your specific proxy platform, means your access control policy will hold up under both daily operational use and formal security scrutiny. That is what subnet-based planning delivers that per-IP management never can: a policy that reflects the real structure of your network and stays accurate as that structure changes.