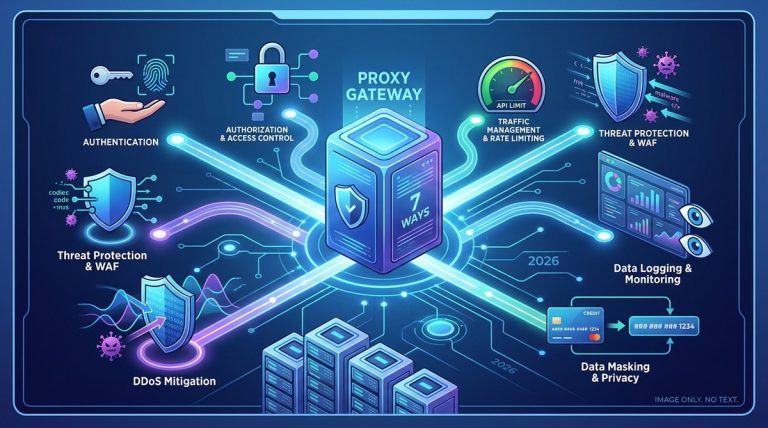
You are responsible for securing the pathways between your microservices and the outside world. Every API call is a potential entry point for an attacker, and every misconfigured route can expose sensitive data. That is where proxy server API gateway management comes into play. A proxy server sitting in front of your APIs can handle traffic routing, enforce security policies, and provide a single point of control for your entire microservice ecosystem. This guide walks through seven practical ways to use proxy servers for secure API gateway management in 2026, with real configuration advice and common pitfalls to avoid.
A proxy server is not just a traffic cop. It is your first line of defense for API security. By routing all external requests through a reverse proxy, you can apply rate limiting, enforce TLS termination, validate JWTs, and log every transaction in one place. This article shows seven concrete ways to set that up for your microservices architecture in 2026, with step-by-step examples and a comparison table to help you choose the right approach.
Why Your API Gateway Needs a Proxy Server
Your microservices talk to each other and to external clients. Without a proxy server in front, every service must handle authentication, rate limiting, and SSL termination on its own. That is a maintenance headache and a security risk. A reverse proxy acts as a single entry point. It inspects all incoming traffic, strips malicious payloads, and forwards only clean requests to your backend services. This pattern is standard in 2026 for any serious deployment.
A proxy server also hides your internal network topology. Attackers cannot directly probe your application servers because they only see the proxy. This reduces your attack surface significantly.
1. Use a Reverse Proxy for Centralized Routing and TLS Termination
The most common pattern is to place a reverse proxy like Nginx, HAProxy, or a cloud-based proxy in front of your API gateway. The proxy handles TLS termination, so your backend services do not need to manage certificates. This simplifies certificate renewal and reduces CPU load on your application servers.
Here is how to set it up:
- Install Nginx on a dedicated server or container.
- Configure an upstream block that points to your API gateway.
- Set up a server block that listens on port 443 with your SSL certificate.
- Proxy all requests to the upstream with the
proxy_passdirective. - Add headers like
X-Forwarded-Forso your API knows the original client IP.
upstream api_gateway {
    server api-gateway.internal:8080;
}

server {
    listen 443 ssl;
    ssl_certificate /etc/ssl/certs/yourdomain.crt;
    ssl_certificate_key /etc/ssl/private/yourdomain.key;

    location / {
        proxy_pass http://api_gateway;
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    }
}
This configuration offloads TLS from your API gateway and gives you a single point to rotate certificates. For more on this pattern, see how to deploy a reverse proxy for improved network security.
2. Enforce Rate Limiting at the Proxy Level
Without rate limiting, a single client can overwhelm your API gateway with requests. This can lead to denial of service for other users and drive up your infrastructure costs. A proxy server can enforce rate limits before traffic even reaches your application logic.
In Nginx, you can use the limit_req module:
http {
    limit_req_zone $binary_remote_addr zone=api_limit:10m rate=10r/s;

    server {
        location /api/ {
            limit_req zone=api_limit burst=20 nodelay;
            proxy_pass http://api_gateway;
        }
    }
}
This limits each IP address to 10 requests per second with a burst of 20. Requests beyond that get a 503 response. Adjust the rate based on your expected traffic patterns.
You can also implement rate limiting by API key if your proxy supports Lua scripting or has a plugin system. This is a common requirement for why your proxy server needs rate limiting to stop API abuse.
3. Validate JWTs and API Keys Before They Reach Your Services
Authentication checks at the proxy level prevent unauthorized requests from ever touching your backend. This reduces load on your application servers and stops attackers before they can exploit vulnerabilities in your API logic.
A proxy can validate JSON Web Tokens by checking the signature and expiration. Here is a simplified approach using OpenResty (Nginx with Lua):
access_by_lua_block {
    local jwt = require("resty.jwt")
    local token = ngx.var.http_authorization
    if token then
        token = token:gsub("Bearer ", "")
        local jwt_obj = jwt:verify("your-secret-key", token)
        if not jwt_obj.verified then
            ngx.status = 401
            ngx.say("Unauthorized")
            ngx.exit(ngx.HTTP_UNAUTHORIZED)
        end
    else
        ngx.status = 401
        ngx.exit(ngx.HTTP_UNAUTHORIZED)
    end
}
For API key validation, you can check against a local cache or an internal authentication service. This keeps the validation fast and removes the need for every microservice to implement its own auth logic.
If you are building a custom solution, check out how to build a custom proxy server for internal devops pipelines.
4. Log and Monitor All API Traffic from a Single Point
Centralized logging is a major advantage of proxy server API gateway management. Every request passes through the proxy, so you can capture method, path, status code, response time, and client IP in one place.
Configure structured logging in your proxy:
log_format api_log '$remote_addr - $remote_user [$time_local] '
                   '"$request" $status $body_bytes_sent '
                   '"$http_referer" "$http_user_agent" '
                   '$request_time';

access_log /var/log/nginx/api_access.log api_log;
Feed these logs into a centralized system like Elasticsearch or a cloud logging service. This allows you to build dashboards for API performance and detect anomalies. For deeper analysis, read about why your proxy server logs are a goldmine for network security analytics in 2026.
A table of common logging fields and their uses:
| Field | Example | What It Tells You |
|---|---|---|
| Client IP | 203.0.113.45 | Where the request originated |
| Request URI | /api/v2/users | Which endpoint was called |
| Status Code | 401 | Authentication failure rate |
| Response Time | 0.235 | Backend latency issues |
| User Agent | curl/7.68.0 | Client type, potential bot detection |
5. Implement Request and Response Transformation
Sometimes your backend services expect data in a specific format, but external clients send something different. A proxy can transform requests and responses on the fly. This includes adding or removing headers, rewriting paths, or converting between XML and JSON.
For example, you might need to strip sensitive headers before forwarding to your backend:
proxy_hide_header X-Powered-By;
proxy_hide_header Server;
proxy_set_header X-Request-ID $request_id;
You can also rewrite URLs. If your internal service listens on /v1/, but your public API uses /v2/, the proxy can translate:
location /v2/ {
    rewrite ^/v2/(.*) /v1/$1 break;
    proxy_pass http://api_gateway;
}
This keeps your internal API versioning independent from your public contract. For more on header security, see why your proxy may be leaking HTTP headers and how to fix it.
6. Route Traffic Based on Content or Client Type
A proxy can inspect the request and route it to different backends based on the path, headers, or even the request body. This is useful for blue-green deployments, A/B testing, or separating traffic from mobile and web clients.
Route by path:
location /api/web/ {
    proxy_pass http://web_backend;
}

location /api/mobile/ {
    proxy_pass http://mobile_backend;
}
Route by header:
if ($http_x_client_type = "mobile") {
    proxy_pass http://mobile_backend;
}
This pattern lets you deploy different versions of your API to different client groups without changing the public endpoint. It also helps with 5 best practices for load balancing with proxy servers in 2026.
7. Cache Responses to Reduce Load on Your Backend
Caching at the proxy level can dramatically reduce the number of requests that reach your API gateway. For idempotent GET endpoints, the proxy can store the response and serve it directly for a configurable time.
Enable caching in Nginx:
proxy_cache_path /data/nginx/cache levels=1:2 keys_zone=api_cache:10m max_size=1g;

server {
    location /api/ {
        proxy_cache api_cache;
        proxy_cache_key "$scheme$request_method$host$request_uri";
        proxy_cache_valid 200 5m;
        proxy_cache_use_stale error timeout updating;
        proxy_pass http://api_gateway;
    }
}
This caches successful responses for five minutes. Adjust the proxy_cache_valid directive based on how stale your data can be. For endpoints that return user-specific data, disable caching by setting proxy_no_cache based on cookies or headers.
If you want to optimize your caching strategy, see how to configure a proxy server for caching and bandwidth optimization in 2026.
Common Mistakes in Proxy Server API Gateway Management
Even experienced teams make errors when setting up a proxy for API management. Here are the most common ones:
- Not validating upstream certificates. If your proxy connects to your backend over HTTPS, verify the certificate. Otherwise, a man-in-the-middle attack inside your network is possible.
- Exposing internal headers. Headers like
X-Forwarded-Forcan be spoofed if your proxy does not clear them before forwarding. Always set them from the proxy itself. - Relying on client IP for rate limiting behind a CDN. If you use a content delivery network, the IP you see is the CDN node, not the client. Use the
X-Forwarded-Forheader instead, but validate it. - Forgetting to set timeouts. Without proper proxy timeouts, a slow backend can hold connections open indefinitely, exhausting server resources.
Expert advice: Always test your proxy configuration in a staging environment that mirrors production. Use tools like
curlwith verbose output andnginx -tto catch syntax errors. A misconfigured proxy can take down your entire API surface faster than any attacker. For a full checklist, read 7 essential proxy security checks every IT admin should run in 2026.
Choosing Between Proxy Configurations
Not every setup fits every team. Here is a comparison of common proxy server API gateway management approaches:
| Approach | Best For | Tradeoff |
|---|---|---|
| Nginx reverse proxy | Teams that need high performance and flexibility | Requires manual configuration and Lua for advanced logic |
| HAProxy | High-traffic environments with TCP and HTTP routing | Less built-in caching support |
| Cloud API gateway (AWS, GCP) | Teams that want managed infrastructure | Vendor lock-in and higher cost at scale |
| Kong or Tyk (open source) | Teams that need plugin-based extensibility | More complex initial setup |
| Custom proxy (Go, Rust) | Teams with very specific performance needs | High development and maintenance cost |
For most mid-to-large companies, Nginx or a managed cloud gateway is the right starting point. You can always migrate later.
Putting It All Together for Your Microservices
Start with a single reverse proxy that handles TLS termination and routing. Add rate limiting and JWT validation next. Then enable logging and monitoring. Finally, layer in caching and content-based routing as your traffic grows.
Each step builds on the previous one. You do not need to implement all seven techniques at once. Pick the ones that solve your most pressing problem today. For most teams, that is rate limiting and authentication.
If you are unsure where to begin, start with how to choose the best proxy server for your network security needs. Then move on to optimizing proxy server performance for enterprise networks as your traffic scales.
The Proxy Is Your API’s Best Security Layer
A proxy server is not an optional extra for your API gateway. It is a core component of a secure microservices architecture. By centralizing routing, authentication, rate limiting, and logging, you reduce complexity and improve security at the same time. The seven techniques covered here give you a practical starting point for 2026. Try one this week. See how it changes your incident response time and your team’s confidence in the system. Your future self, and your users, will thank you.