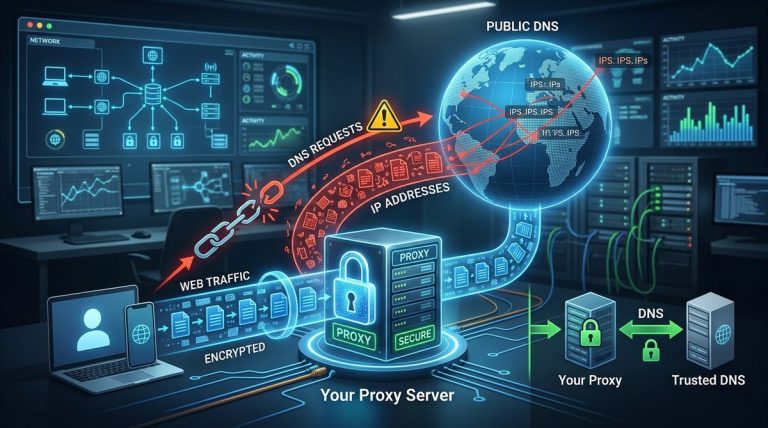
Your proxy server is doing its job. Your VPN tunnel is up. Your IP address is hidden. But are your DNS queries still slipping out the back door? That is the silent privacy killer most sysadmins miss. A single leaked DNS query can reveal every website you visit to your Internet Service Provider, even when your traffic looks perfectly anonymized. If you manage a corporate network or run a personal VPN, you need a reliable DNS leak test to know for sure.
A DNS leak test reveals whether your system is sending domain lookups outside your proxy or VPN tunnel. If it is, your ISP or anyone watching your network can see every site you visit. This guide walks you through running the test, interpreting the results, and applying targeted fixes to seal the leak for good.
What a DNS Leak Actually Looks Like
Picture this scenario. You connect to a corporate proxy in another office. You load a website. Your browser sends the request through the proxy. But before it does that, your operating system asks your local DNS resolver for the IP address of that website. That DNS query travels over your default internet connection, not through the proxy. Your real IP stays hidden for the web traffic, but the DNS lookup leaks your location and your browsing habits to your ISP or any eavesdropper on the local network.
A DNS leak test catches this exact behavior. It sends a request to a test server and checks which DNS resolvers handled the lookup. If the test shows a resolver from your local ISP instead of the one your proxy or VPN should be using, you have a leak.
Why Standard Proxy and VPN Setups Leak
Leaks happen for a few predictable reasons. Understanding them helps you know where to look when your DNS leak test comes back dirty.
- System DNS configuration overrides proxy settings. Your browser might honor the proxy for HTTP and HTTPS traffic, but your operating system still uses its own DNS resolver for the initial domain lookup.
- VPN split tunneling misconfiguration. If your VPN is set to split tunnel, DNS traffic can bypass the tunnel and use your local gateway.
- IPv6 traffic bypass. Many proxies and VPNs only handle IPv4. If your system has IPv6 enabled, DNS queries can travel over IPv6 without going through the proxy at all.
- Third-party applications ignoring system settings. Some apps hardcode their own DNS resolution and skip your proxy or VPN entirely.
How to Run a DNS Leak Test in Three Steps
You do not need expensive tools. A browser and a few command line utilities are enough. Follow these steps to run your own DNS leak test.
-
Note your assigned DNS resolvers. Before you connect to your proxy or VPN, check your current DNS servers. On Windows, run
ipconfig /alland look for the DNS Servers line. On macOS or Linux, runcat /etc/resolv.confornmcli dev show. Write these IP addresses down. They are your baseline. -
Connect to your proxy or VPN. Establish your usual connection. Make sure your proxy is active or your VPN tunnel is up.
-
Visit a DNS leak test website. Go to a trusted DNS leak test page. The site will show you the IP addresses of the DNS resolvers that handled your request. Compare them to your baseline list. If they match your baseline, your DNS queries are leaking. If they show different resolvers (like Cloudflare or Quad9), your proxy or VPN is handling DNS correctly.
You can also verify from the command line. Use nslookup example.com and check which server responded. If the responding server is your local ISP resolver instead of the one your proxy should use, you have a confirmed leak.
Common Leak Scenarios and Their Fixes
The table below maps typical leak causes to their solutions. Use it as a reference when your DNS leak test flags a problem.
| Scenario | What Happens | How to Fix It |
|---|---|---|
| Proxy set in browser only | Browser routes HTTP through proxy, but DNS still uses local resolver | Configure a system-wide proxy or use a PAC file that includes DNS resolution |
| VPN split tunneling enabled | DNS queries travel over the local internet connection | Disable split tunneling for DNS traffic, or route all traffic through the VPN |
| IPv6 enabled with no proxy support | DNS queries leak over IPv6 while proxy handles IPv4 only | Disable IPv6 on the client or configure the proxy to handle IPv6 DNS |
| Application ignores system proxy | App performs its own DNS resolution outside the proxy | Force the app to use the system proxy, or route its traffic through a local forwarding service |
Tools That Help You Detect Leaks Automatically
Running manual tests is fine for a one-time check, but if you manage multiple machines or a corporate network, you want automation. Several tools can perform a DNS leak test on a schedule and alert you when something changes.
- dnscrypt-proxy includes a diagnostic mode that logs every outgoing DNS query and shows whether it is encrypted or plaintext.
- Wireshark can capture DNS traffic on your network interface. Filter for
dnsand look for packets going to port 53 that do not reach your proxy. - Pi-hole with its query log shows every domain lookup on your network. If you see lookups from a machine that should be proxied, you have a leak.
- Custom scripts using
digornslookupcan compare expected resolver IPs against actual resolver IPs and send you a notification on mismatch.
A single DNS leak can undo months of careful proxy configuration. Test after every change to your network stack, not just during initial setup. This habit alone saves sysadmins countless hours of troubleshooting later.
Five Configuration Mistakes That Cause DNS Leaks
Even experienced IT professionals make these mistakes. Watch for them when you run your DNS leak test.
- Hardcoding DNS servers in the network adapter settings instead of letting the proxy or VPN assign them dynamically.
- Using a public DNS resolver like 8.8.8.8 on the client while expecting the proxy to handle resolution. The client will use the hardcoded resolver first.
- Forgetting to update the DNS settings after switching from a VPN to a proxy. Old resolver entries remain active.
- Configuring the proxy only in the browser while leaving other applications like email clients, update services, and chat apps unproxied. Those apps perform their own DNS lookups.
- Assuming that enabling a VPN automatically secures DNS. Many VPN providers do not force DNS through the tunnel unless you explicitly enable that option.
How to Seal the Leak Permanently
Once your DNS leak test confirms a problem, you need to fix the root cause. Here is a reliable approach that works for most setups.
First, force all DNS traffic through your proxy or VPN. On Windows, you can use a tool like dnscrypt-proxy to encrypt and forward all DNS queries. On Linux, configure systemd-resolved to use your proxy’s DNS server exclusively. On macOS, set the DNS servers in the network interface to point to a local forwarding service that routes through the proxy.
Second, disable IPv6 if your proxy does not support it. You can do this in the network adapter settings or via a system policy. Many corporate proxies still lack full IPv6 support, and that gap is a common leak vector.
Third, use a firewall rule to block all outgoing DNS traffic that does not go to your proxy. On Linux, iptables or nftables can drop packets destined for port 53 on any interface except the tunnel interface. On Windows, a simple outbound firewall rule can achieve the same result.
Fourth, test again. Run your DNS leak test after each change. Do not assume the fix worked. Verify it.
Building a Regular Testing Habit
A DNS leak test is not a one-and-done task. Network configurations change. Software updates reset settings. New devices join the network. Schedule a test every month, or after any significant change to your firewall, proxy, or VPN setup.
You can automate this. A cron job or scheduled task that runs a DNS leak test and emails you the result takes ten minutes to set up and saves you from silent leaks that go unnoticed for weeks.
For enterprise environments, consider integrating DNS leak detection into your broader security monitoring. Tools like can alert you when DNS behavior deviates from the baseline. Pair that with https://winproxy.net/best-practices-for-securing-your-network-against-modern-threats/ to build a defense that covers all the angles.
Your Privacy Depends on This One Test
Think of a DNS leak test as the smoke detector for your network privacy. You can have the best proxy server in the world, the strongest encryption, and the most locked-down firewall, but if DNS is leaking, you are broadcasting your browsing history to anyone who cares to listen.
Take ten minutes right now. Run the test. Compare the resolvers. If you see your ISP’s DNS server in the results, you know exactly what to fix. If everything looks clean, you get the peace of mind that your privacy setup is actually working the way you intended. Either way, you walk away with a stronger, more honest understanding of your network’s real security posture.